Build Business Website Security One Layer at a Time
Build Business Website Security One Layer at a Time
Business website security is easier to manage as a set of owned decisions. A small company may not control its hosting platform's infrastructure, but it does control who edits the site, what its forms request, which services are connected, and when those choices are reviewed.
That shared-responsibility view makes implementing website security best practices practical. Platform safeguards matter, but protecting customer information online remains a business duty across accounts, content, data choices, and integrations. Protecting customer information online, preventing unauthorized website access, and monitoring security vulnerabilities regularly then become normal operating work instead of a once-a-year emergency.
Business website security starts with a five-line inventory
First, list what the website could expose or disrupt: the Strikingly account, domain, teammate access, form submissions, contact records, connected services, custom code, and external widgets. Business website security improves when each item has an owner who can justify or remove it.
Record these five details for every website asset
- Asset: the account, form, domain, script, integration, or data set.
- Purpose: why it is needed and the minimum information required.
- Owner: the person responsible for access, updates, and incidents.
- Protection: the control, such as HTTPS, restricted permissions, or retention.
- Review date: when the owner will confirm that it is still necessary.
This inventory supports protecting customer information online because forgotten forms and abandoned integrations become visible. It also makes monitoring security vulnerabilities regularly specific: the team knows where to look, who responds, and what normal looks like. Implementing website security best practices starts with that clarity and a checklist shaped around the actual system.
Secure the connection before requesting information

Strikingly Free HTTPs Feature
HTTPS encrypts information moving between a browser and the website. Strikingly states that HTTPS and SSL are automatically enabled for Strikingly sites, including custom-domain sites. Confirm the secure connection on the public domain after changing domain settings. For business website security, a loaded page still fails if its customer-facing address shows a certificate warning.
Protecting customer information online also requires checking external content. An image, script, iframe, or form served over HTTP can create mixed-content warnings. Replace it with an HTTPS version and remove resources without owners. Implementing website security best practices means testing the whole page instead of assuming one certificate covers every embed.
Repeat the check after adding an integration, moving a domain, or changing a checkout or booking service. Monitoring security vulnerabilities regularly should prioritize pages that request sensitive information. Business website security is strongest when encryption is verified where data is submitted.
Make editor access narrow, named, and temporary
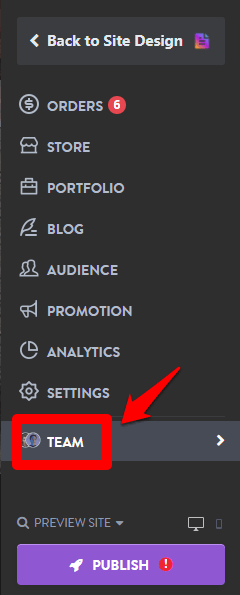
Strikingly Team Settings Panel
Everyday access risk often begins with shared passwords, former contractors, or reused credentials. Preventing unauthorized website access starts with a unique password in a reputable password manager. Protect the recovery email and enable multi-factor authentication on that email or identity service when available. Authentication controls differ by service, so verify what each account actually supports.
Use Strikingly's teammate roles and publish permissions instead of passing one owner login around. An editor, blogger, store manager, or support agent should receive only the access needed for current work. Preventing unauthorized website access also means removing a teammate promptly after a project ends and reviewing administrator privileges after staff changes.
Keep an access register with each person's name, role, reason, approval date, and removal date. It makes monitoring security vulnerabilities regularly concrete because an unexpected editor is immediately visible. Implementing website security best practices here means ending anonymous, permanent access. Business website security needs accountability for anyone who can change content, forms, domains, or store settings.
Use page passwords for a limited access problem
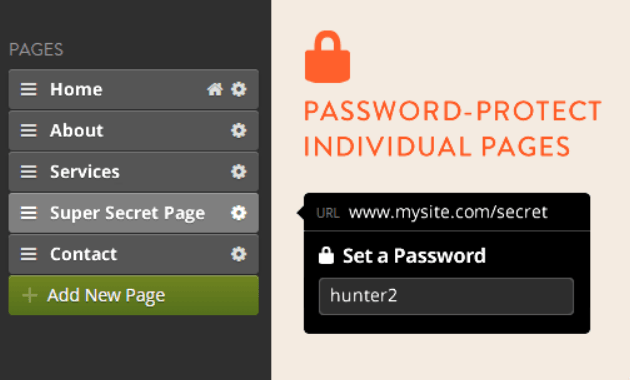
Strikingly Password Protection
Strikingly Pro users can apply password protection to a site or individual page. It suits a private event, early client review, or temporary material for a known group. Preventing unauthorized website access means sharing the password through a trusted separate channel, changing it with membership, and removing the gate when the private phase ends.
A page password is an access gate, not a secure records repository. Do not publish identity documents, payment details, medical information, or confidential customer files merely because a page has one shared password. Protecting customer information online requires choosing systems designed for the sensitivity and legal obligations of that data. Business website security depends on matching the control to the risk instead of stretching a convenient feature beyond its purpose.
Document who receives the password and why. Preventing unauthorized website access becomes harder when a shared secret circulates indefinitely, so set an expiry decision before publishing. Monitoring security vulnerabilities regularly should include confirming that protected pages still need to exist and that their links have not been exposed in public copy or campaigns.
Protecting customer information online starts with collecting less
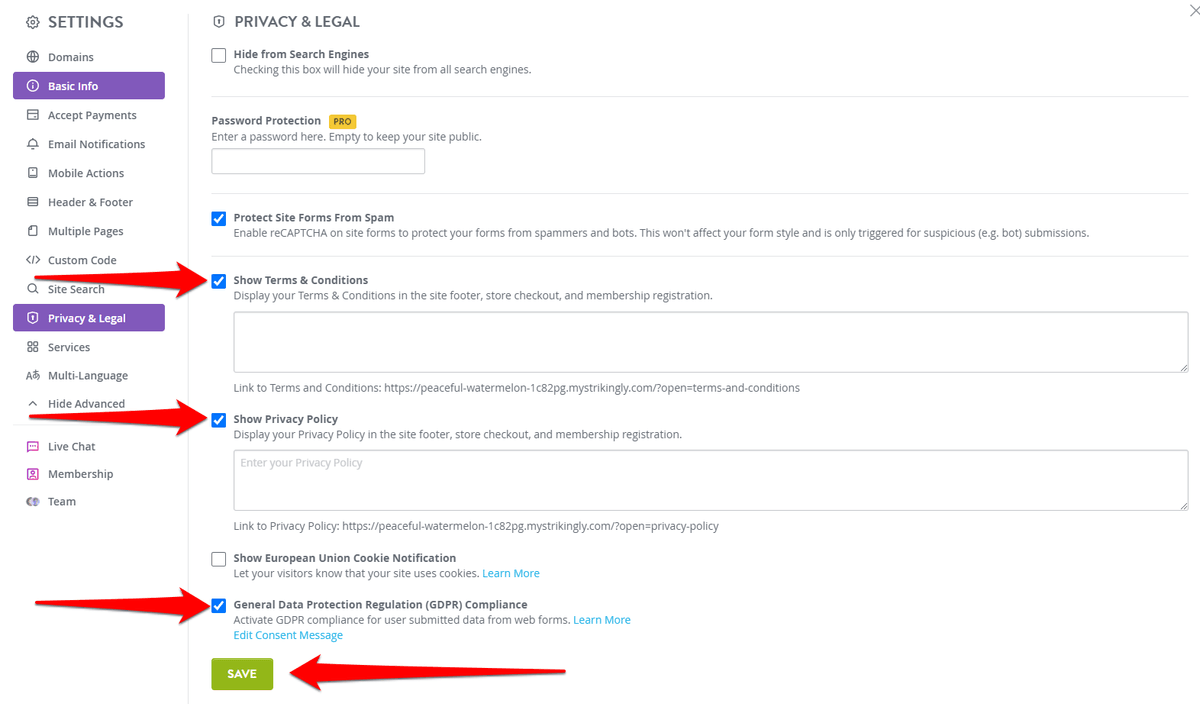
Strikingly GDPR Compliance Setting
The safest unnecessary customer field is the one never collected. Review every custom form and ask whether each answer is required. Protecting customer information online may mean narrowing a free-text box, removing birth dates from an inquiry, or waiting for a secure later stage to request sensitive details. Shorter forms can also clarify the purpose.
Tell people how their information will be used, who receives it, and how to ask questions. Strikingly explains how to add a privacy policy or terms page, while its GDPR compliance settings can add form consent controls and a cookie notice. Laws vary, so seek qualified legal advice for applicable obligations.
Protecting customer information online continues after submission. Restrict who can view or export site contacts, establish a retention period, and delete records that no longer have a legitimate purpose. Implementing website security best practices should connect the public form to the internal handling process. Preventing unauthorized website access matters at both ends: the page that collects data and the account where staff later manage it.
Implementing website security best practices across external services
PEAPLE Template from Strikingly
Widgets, analytics tags, scheduling tools, advertising pixels, and custom scripts can change the website's risk. Business website security therefore needs a third-party register recording the vendor, purpose, data received, owner, renewal date, and removal method. Use minimum permissions when preventing unauthorized website access across connected accounts.
Implementing website security best practices includes checking whether an integration remains useful after its campaign or owner is gone. Remove dormant scripts, revoke unused API keys at their issuing service, and verify that remaining embeds use HTTPS. Protecting customer information online is easier when fewer companies receive it; preventing unauthorized website access is easier when fewer external accounts can affect the journey.
Monitoring security vulnerabilities regularly also means reviewing vendor notices and ownership changes. A service that was acceptable last year may change its data practices, stop receiving updates, or become unnecessary, so document the decision to retain or remove it.
Use Strikingly's own privacy policy, GDPR statement, and terms of service to understand the platform relationship, then separately assess every tool the business adds. Business website security cannot be delegated through assumption; the owner must know where information travels after a visitor clicks submit.
Use ownership when monitoring security vulnerabilities regularly
Monitoring security vulnerabilities regularly does not require becoming a penetration tester. It requires reviewing the controls the business owns. Monthly, confirm HTTPS, teammate access, important forms, and integration ownership. Quarterly, revisit the data inventory, privacy explanation, page passwords, and response contacts. This schedule keeps implementing website security best practices tied to observable evidence.
A monthly routine for monitoring security vulnerabilities regularly
- Test the domain lock indicator, key forms, and protected pages.
- Compare teammates with the register and remove obsolete permissions.
- Check scripts, embeds, and tools against the third-party register.
- Review account alerts, suspicious messages, and unexpected changes.
- Record each finding, owner, due date, and verified fix.
Monitoring security vulnerabilities regularly includes escalation. If a message imitates Strikingly or requests credentials, avoid its links, verify through a known address, and follow Strikingly's guidance for identifying and reporting phishing. If customer data may be exposed, preserve evidence, restrict access, contact appropriate professionals, and follow applicable notification requirements.
Preventing unauthorized website access becomes more reliable when the review produces named actions rather than a vague security score. Protecting customer information online becomes measurable when the team can show which fields were removed, who retains access, and when old records were deleted. Implementing website security best practices becomes sustainable when fixes enter the same task system used for marketing and operations.
Keep the baseline visible as the website changes
A growing site will add pages, teammates, forms, and services. Implementing website security best practices during each change means identifying the asset, assigning an owner, choosing minimum access, documenting the data path, and scheduling review. Business website security education can draw on Strikingly's security guidance, but the company's own inventory remains the practical source of truth.
Use the five-line inventory before each launch. Ask what information the page collects, who can change it, which outside services receive data, what a visitor is told, and when the setup will be checked again. That habit links preventing unauthorized website access with protecting customer information online instead of treating them as unrelated projects.
Implementing website security best practices is not a promise that nothing will ever go wrong. It is a disciplined way to reduce avoidable exposure and respond faster when something changes. Monitoring security vulnerabilities regularly keeps the baseline current, while business website security becomes a visible business responsibility with owners, dates, and evidence rather than a box checked at launch.
